Well, it depends.
When it comes to data protection and security, there is often a major difference between what an organisation is legally permitted to do with personal data and what its customers believe it should do.
And just because an organisation has the right to use someone’s data in a particular way doesn’t necessarily mean it should.
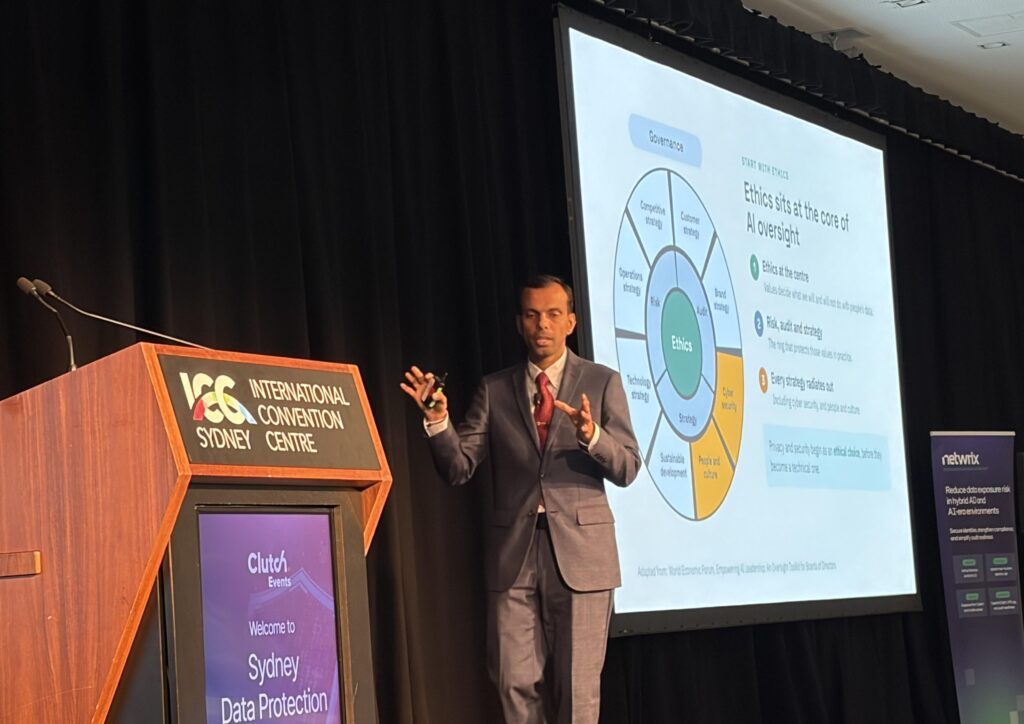
This tension between innovation, compliance, and customer expectations was one of the key themes of Clutch Events’ recent Data Protect and Security Summit in Sydney, where leaders in privacy, security, and data protection came together to discuss the intricacies of keeping data safe and secure.
As has been common at Clutch events recently, the key themes were highlighted in the final Think Tank session of the day, which focused on questions of permission, transparency, and ethics.
Those customer expectations can vary significantly depending on the type of organisation involved and the social licence that it carries. As has so often been proven, a fast-moving digital business that has staked its value on growth at all costs can get away with behaviours that a solid, stable, and trusted organisation would never dream of.
While this doesn’t mean any organisation is exempt from the law, the boundaries of acceptable behaviour can be very different.
On the flip side, it is also possible for more stable and trusted organisations to tick every box when it comes to regulatory compliance and still fall foul of public opinion when their actions fail to reflect consumer expectations, or when they fall victim to a data exfiltration attack despite their best efforts.
The discussion also touched on another key issue, namely the extent to which organisations can offload their responsibilities onto consumers through the use of complex consent documents. These documents tend to push consumers and employees into signing away rights and protections they should reasonably expect to retain over how their data is used.
While the push for plain English consent language has gained momentum in the past year, it is still far from common practice. If a consent document needs a lawyer to write it, then it probably requires a lawyer to interpret it, and has already failed the plain English test. Yes, it needs to stand up to legal requirements and scrutiny, but that should not be used as a smokescreen to give organisations an open licence to use people’s data as they choose.
This issue is likely to gain greater attention as we move into the era of personal AI agents, especially when those agents are supplied by organisations whose chief business model is to collect and monetise personal data. Who is that personal agent really working for?
Unfortunately, the companies at the forefront of developing such services are also among those whose pursuit of innovation-fuelled growth is likely to see them push the boundaries of what is legally permissible, let alone what is socially acceptable. ‘Move fast and break things’ is a fantastic strategy when the penalties are a rounding error compared to quarterly revenue – but possibly not so socially acceptable when the things you break are people.
Australia is equipped with a cohort of passionate, talented, and highly concerned professionals who are very much aware of the differences between what an organisation can do with personal data and what it should do.
The challenge now is ensuring those voices are heard early and loudly enough to shape innovation, rather than being left to sort through the mess after the damage has been done.
On that, we all depend.